
Cyber threats today are more advanced and targeted than ever. Traditional security tools alone are no longer enough to stop real-world attacks.
This is where red teaming becomes important. It simulates real cyberattacks to test how well an organization can detect and respond.
At its core, red teaming uses adversary simulation. This means security experts act like real attackers, using the same tactics and strategies.
This guide explains what red teaming is, how it works, and why it is essential for modern cybersecurity.
What Is Red Teaming?
Definition
Red teaming is a cybersecurity practice where ethical hackers simulate real-world cyberattacks to test an organization’s security defenses.
Instead of just scanning for vulnerabilities, red teaming focuses on how an attacker would actually break into systems, move within networks, and access sensitive data.
Key Idea
The main idea behind red teaming is simple:
Think like an attacker, not a defender
Red teamers use the same mindset, tools, and techniques as real hackers to:
- Identify hidden vulnerabilities
- Exploit weaknesses in systems and processes
- Test how security teams respond to attacks
This approach provides a realistic view of an organization’s security posture.
What Is Adversary Simulation?
Adversary simulation is a core concept within red teaming. It involves mimicking the behavior of real cyber attackers to test how well an organization can defend itself.
Unlike traditional testing, adversary simulation focuses on:
- Real attacker tactics and techniques
- Long-term attack scenarios
- Multi-step intrusion strategies
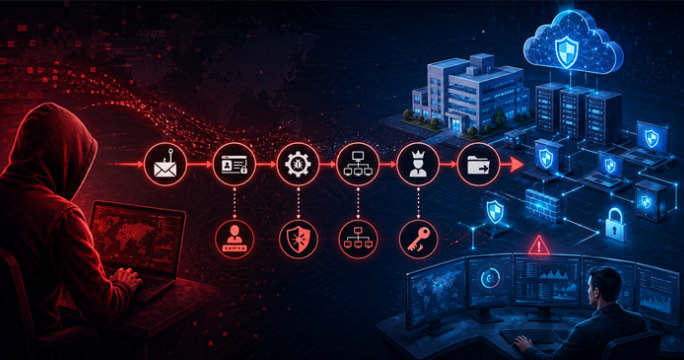
For example, instead of just testing a single vulnerability, an adversary simulation may:
- Start with phishing
- Gain initial access
- Move laterally across systems
- Escalate privileges
- Attempt data exfiltration
This makes red teaming far more realistic and effective compared to basic security testing.
Red Team vs Blue Team vs Purple Team
In cybersecurity, different teams play different roles in protecting an organization. Understanding the difference between red team, blue team, and purple team helps clarify how red teaming fits into the bigger security strategy.
Red Team
The red team acts as the attacker. Their goal is to simulate real-world cyberattacks and identify weaknesses in the system.
They focus on:
- Exploiting vulnerabilities
- Bypassing security controls
- Testing how far they can penetrate systems
- Mimicking real attacker behavior
Red teams use adversary simulation to replicate real threats and uncover hidden risks.
Blue Team
The blue team is responsible for defending the organization. They monitor systems, detect threats, and respond to attacks.
Their responsibilities include:
- Monitoring security alerts
- Detecting suspicious activity
- Responding to incidents
- Strengthening defenses
While the red team attacks, the blue team protects.
Purple Team
The purple team combines both red and blue teams. Their goal is collaboration.
Instead of working separately, they:
- Share insights between attack and defense teams
- Improve detection capabilities
- Strengthen overall security posture
- Learn from simulated attacks
Purple teaming helps organizations turn red team findings into real defensive improvements.
Why Red Teaming Is Important
Modern cyberattacks are not simple. Attackers use advanced techniques, multiple entry points, and long-term strategies to breach systems. Traditional security testing often fails to detect these complex threats.
This is why red teaming is important. It provides a realistic view of how an actual attack would impact an organization.
Identifies Real-World Vulnerabilities
Red teaming goes beyond basic scanning. It uncovers weaknesses that only appear during real attack scenarios.
These may include:
- Misconfigured systems
- Weak access controls
- Hidden network vulnerabilities
By simulating real attacks, organizations can identify risks that traditional tools often miss.
Tests Detection and Response
One of the biggest benefits of red teaming is testing how well security teams respond to threats.
It helps answer questions like:
- Can the team detect the attack?
- How quickly do they respond?
- Are the response processes effective?
This improves incident response readiness.
Exposes Human and Process Weaknesses
Cybersecurity is not just about technology. People and processes also play a major role.
Red teaming can expose:
- Employee susceptibility to phishing
- Poor internal security practices
- Weak communication during incidents
This helps organizations improve both technical and human defenses.
Goes Beyond Automated Tools
Automated tools can identify known vulnerabilities, but they cannot think like an attacker.
Red teaming uses adversary simulation to:
- Combine multiple attack methods
- Exploit chained vulnerabilities
- Adapt strategies in real time
This makes it far more effective than traditional testing.
How Red Teaming Works (Process)
Red teaming follows a structured process designed to simulate real-world cyberattacks. Each phase focuses on how attackers actually operate, making the test realistic and effective.
Step 1: Planning and Scope
The process begins with defining the objectives and scope of the engagement.
This includes:
- Identifying target systems or assets
- Defining attack scenarios
- Setting rules and limitations
- Aligning goals with business risks
A clear scope ensures the red team focuses on meaningful security gaps.
Step 2: Reconnaissance
In this phase, the red team gathers information about the target.
This may include:
- Publicly available data (OSINT)
- Employee information
- Network structure
- Technology stack
Reconnaissance helps attackers understand the environment before launching an attack.
Step 3: Attack Simulation
The red team begins simulating real-world attacks using adversary simulation techniques.
Common methods include:
- Phishing campaigns
- Credential harvesting
- Exploiting exposed services
The goal is to gain initial access just like a real attacker.
Step 4: Exploitation and Lateral Movement
Once inside the system, the red team attempts to expand access.
This includes:
- Escalating privileges
- Moving across systems
- Accessing sensitive data
- Avoiding detection
This phase tests how far an attacker can go within the network.
Step 5: Reporting and Analysis
After the simulation, the red team provides a detailed report.
The report includes:
- Attack paths used
- Vulnerabilities discovered
- Security gaps identified
- Recommendations for improvement
This helps organizations strengthen defenses and improve response strategies.
Types of Red Teaming
Red teaming can be performed in different ways depending on the organization’s goals, infrastructure, and threat landscape. Each type focuses on simulating specific attack scenarios to test different areas of security.
External Red Teaming
External red teaming focuses on testing systems that are exposed to the internet.
This includes:
- Public websites
- External servers
- Cloud applications
- Email systems
The goal is to simulate how an outside attacker would try to gain access to the organization without any internal knowledge.
Internal Red Teaming
Internal red teaming assumes that the attacker already has access to the internal network.
This could simulate:
- A compromised employee account
- A malicious insider
- A breached internal system
The objective is to test how far an attacker can move within the organization and access sensitive data.
Social Engineering
Social engineering focuses on human vulnerabilities rather than technical ones.
Common techniques include:
- Phishing emails
- Fake login pages
- Phone-based scams
- Impersonation attacks
This type of adversary simulation tests how employees respond to manipulation and deception.
Physical Security Testing
This type of red teaming evaluates physical access controls within an organization.
It may include:
- Attempting unauthorized entry into offices
- Accessing restricted areas
- Testing security checkpoints
Physical security testing helps identify weaknesses beyond digital systems.
Red Teaming vs Penetration Testing
Many organizations confuse red teaming with penetration testing. While both are important for cybersecurity, they serve different purposes and operate at different levels.
Key Difference
The main difference is:
- Red Teaming → Simulates a full real-world attack
- Penetration Testing → Identifies specific vulnerabilities
Red Teaming
Red teaming focuses on adversary simulation. It mimics how a real attacker would target an organization over time.
Key characteristics:
- Goal-based testing (e.g., access sensitive data)
- Long-term engagement
- Combines multiple attack techniques
- Tests people, processes, and technology
- Focuses on detection and response
Red teaming answers:
Can an attacker actually break in and achieve their objective?
Penetration Testing
Penetration testing focuses on identifying and exploiting known vulnerabilities within a defined scope.
Key characteristics:
- Vulnerability-focused
- Short-term testing
- Limited scope
- Focuses mainly on technical weaknesses
- Provides a list of vulnerabilities
Penetration testing answers:
What vulnerabilities exist in the system?
Comparison Table
| Red Teaming | Penetration Testing |
| Real-world attack simulation | Vulnerability testing |
| Goal-based | Scope-based |
| Long-term engagement | Short-term testing |
| Tests full security posture | Tests specific systems |
| Includes human + process weaknesses | Mostly technical focus |
Common Red Teaming Techniques
During a red teaming engagement, security experts use a combination of techniques to simulate real-world cyberattacks. These techniques are based on actual attacker behavior and are often part of adversary simulation scenarios.
Phishing Attacks
Phishing is one of the most common techniques used in red teaming.
It involves:
- Sending fake emails to employees
- Creating realistic login pages
- Trick users into sharing credentials
This tests how vulnerable employees are to social engineering attacks.
Credential Theft
Red teams attempt to gain access by stealing or guessing login credentials.
This may include:
- Password spraying
- Brute force attacks
- Capturing credentials through phishing
Once credentials are obtained, attackers can access systems as legitimate users.
Network Exploitation
This technique focuses on identifying and exploiting vulnerabilities in networks and systems.
It includes:
- Exploiting open ports
- Targeting outdated software
- Taking advantage of misconfigurations
This helps test how secure the organization’s infrastructure is.
Privilege Escalation
After gaining initial access, attackers try to increase their level of control.
This involves:
- Gaining admin access
- Bypassing security restrictions
- Exploiting system weaknesses
Privilege escalation allows attackers to access sensitive systems and data.
Lateral Movement
Once inside the network, attackers move across systems to expand access.
This includes:
- Accessing other machines
- Compromising additional accounts
- Navigating internal systems
Lateral movement helps attackers reach high-value targets within the organization.
Benefits of Red Teaming
Implementing red teaming provides organizations with a deeper and more realistic understanding of their security posture. Unlike traditional testing methods, it focuses on how real attackers operate, making the results more actionable and impactful.
Realistic Risk Assessment
Red teaming simulates actual cyberattacks using adversary simulation techniques.
This helps organizations:
- Understand real-world attack scenarios
- Identify critical security gaps
- Evaluate true business risk
Instead of theoretical vulnerabilities, businesses get a practical view of how an attack would unfold.
Improved Security Posture
By uncovering hidden weaknesses, red teaming helps organizations strengthen their overall defenses.
It allows teams to:
- Fix vulnerabilities that were previously unnoticed
- Improve system configurations
- Strengthen access controls
This leads to a more resilient and secure infrastructure.
Better Incident Response
Red teaming tests how well security teams detect and respond to attacks.
This helps organizations:
- Improve detection capabilities
- Reduce response time
- Strengthen incident handling processes
Over time, this significantly enhances the organization’s ability to manage real cyber threats.
Identifies Human Weaknesses
Many attacks target people rather than systems.
Red teaming exposes:
- Employee vulnerability to phishing
- Poor security awareness
- Weak internal processes
This allows organizations to improve training and reduce human-related risks.
Supports Compliance and Audits
Many industries require organizations to demonstrate strong security practices.
Red teaming helps by:
- Providing detailed reports
- Demonstrating proactive security efforts
- Supporting compliance requirements
It shows that the organization is actively testing and improving its defenses.
Challenges in Red Teaming
While red teaming is highly effective, it also comes with certain challenges that organizations must consider. Understanding these limitations helps businesses plan better and use red teaming more effectively.
Cost
Red teaming can be more expensive than traditional security testing.
This is because:
- It requires highly skilled experts
- Engagements are longer and more complex
- Multiple attack scenarios are tested
For smaller organizations, cost can be a limiting factor.
Complexity
Red teaming involves advanced techniques and real-world adversary simulation.
This makes it:
- More difficult to plan and execute
- Dependent on expert knowledge
- Challenging to manage internally
Organizations often need external specialists to perform effective red teaming.
Time-Intensive
Unlike quick vulnerability scans, red teaming takes time.
It includes:
- Planning and reconnaissance
- Multi-stage attack simulation
- Detailed reporting
This makes it a longer process compared to penetration testing.
Requires Skilled Professionals
Successful red teaming depends on experienced cybersecurity experts.
It requires professionals who:
- Understand attacker behavior
- Can simulate real-world threats
- Adapt strategies dynamically
Without the right expertise, the effectiveness of red teaming can be limited.
Who Needs Red Teaming
Not every organization needs red teaming at the same level, but it is especially important for businesses handling sensitive data or critical systems.
Enterprises
Large organizations with complex infrastructures benefit the most.
They need red teaming to:
- Identify hidden vulnerabilities
- Test large-scale security systems
- Protect critical assets
Financial Institutions
Banks and fintech companies are prime targets for cyberattacks.
Red teaming helps them:
- Protect financial data
- Test fraud detection systems
- Improve security controls
Healthcare Organizations
Healthcare systems store sensitive patient data.
Red teaming helps:
- Protect medical records
- Identify system vulnerabilities
- Ensure data confidentiality
SaaS and Tech Companies
Technology companies often handle large amounts of user data.
Red teaming helps them:
- Secure cloud environments
- Protect customer information
- Improve system resilience
Government and Public Sector
Government systems are high-value targets.
Red teaming is used to:
- Protect national data
- Test critical infrastructure
- Strengthen security readiness
When Should You Conduct Red Teaming
Knowing when to conduct red teaming is just as important as understanding how it works. Since red teaming is a deep and resource-intensive process, organizations should use it strategically at the right time.
After Major Infrastructure Changes
Organizations should conduct red teaming after significant changes in their systems or infrastructure.
This includes:
- Migrating to cloud environments
- Deploying new applications
- Upgrading network architecture
- Implementing new security tools
These changes can introduce new vulnerabilities that need to be tested through adversary simulation.
Before Compliance Audits
Red teaming is highly useful before regulatory or security audits.
It helps organizations:
- Identify security gaps early
- Fix vulnerabilities before assessment
- Demonstrate proactive security practices
This improves audit readiness and reduces compliance risks.
After Security Incidents
If an organization has experienced a cyberattack or data breach, conducting red teaming can help prevent future incidents.
It allows businesses to:
- Understand how the attack happened
- Test improved defenses
- Validate incident response capabilities
This ensures that previous weaknesses have been properly addressed.
On a Regular Basis
Cyber threats evolve constantly. One-time testing is not enough.
Organizations should conduct red teaming:
- Annually
- After major business changes
- When risk levels increase
Regular testing ensures that security defenses remain effective over time.
Conclusion
Red teaming is one of the most advanced and effective ways to test an organization’s cybersecurity defenses. By simulating real-world attacks through adversary simulation, it provides a clear understanding of how well systems, processes, and people can withstand actual threats.
Unlike traditional testing methods, red teaming focuses on real attacker behavior. It helps organizations identify hidden vulnerabilities, improve detection capabilities, and strengthen incident response strategies.
While it requires time, expertise, and investment, the value it provides is significant. Businesses that implement red teaming gain a deeper level of security insight and are better prepared to handle modern cyber threats.
In today’s threat landscape, red teaming is not just an advanced option. It is becoming an essential part of a strong cybersecurity strategy.
Frequently Asked Questions
What is red teaming in cybersecurity?
Red teaming is a cybersecurity practice where experts simulate real-world attacks to test how well an organization can detect and respond to threats. It helps identify hidden weaknesses using attacker-like strategies.
How is red teaming different from penetration testing?
Red teaming simulates a full cyberattack, while penetration testing focuses on finding specific vulnerabilities. Red teaming tests overall security, including people and processes, not just systems.
Is red teaming necessary for all businesses?
Red teaming is most important for organizations handling sensitive data or critical systems. It helps test real-world security and improve overall protection against advanced threats.
How often should red teaming be done?
Red teaming should be conducted regularly, typically once a year or after major system changes. This ensures security defenses remain effective against evolving cyber threats.